Dark Web Monitoring
The Dark Web Monitoring dashboard provides comprehensive monitoring and analysis of your organization's exposure across dark web sources, breach databases, and public data platforms. This centralized threat intelligence tool consolidates multiple data sources into a unified interface that enables security teams to proactively detect, investigate, and remediate potential security incidents involving exposed credentials, sensitive information, and organizational mentions.
This dashboard exists in both the legacy and new NetSPI Platforms. The only UI change is the removal of the events timeline graph at the top of the page. All other functionality has remained the same.
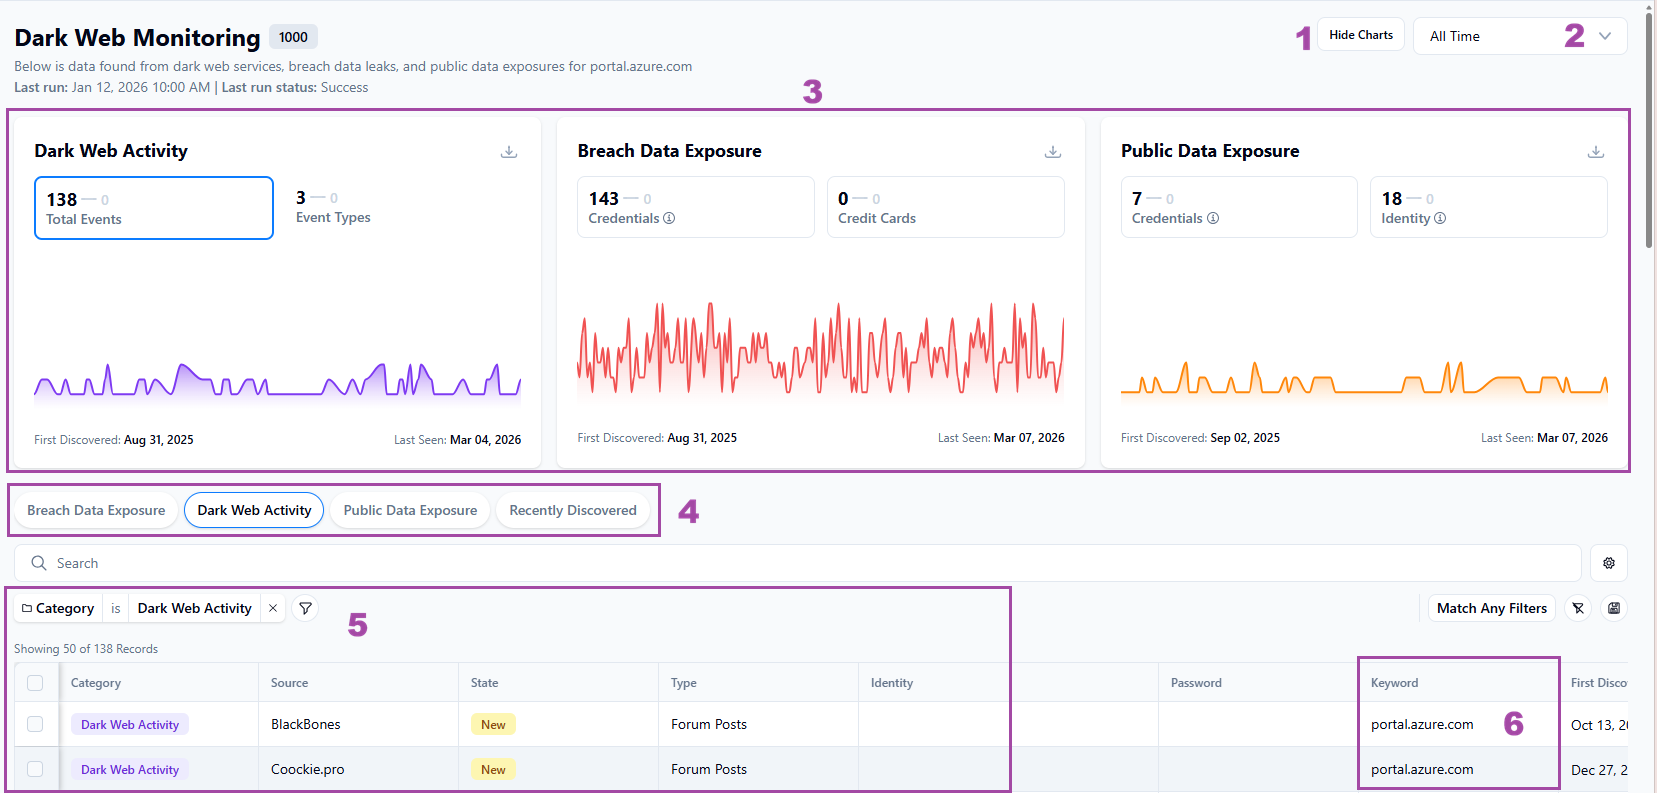
Dark Web Monitoring overview
2. Time range control
Select the time period for which you want to review dark web threat intelligence data. The dashboard supports filtering for the past day, week, month, quarter, all time view, or custom date ranges. Your selection automatically updates all information cards, charts, and the detailed events table to reflect data from the specified period.
The default view displays all time data to provide the most comprehensive threat landscape overview. Changing the time filter updates the events timeline graph, threat summary cards, and all table data to match your selected timeframe.
3. Threat summary charts
The threat summary charts display categorized counts of detected exposures organized by threat type across three primary categories: dark web activity, breach data exposures, and public data leaks.
Each chart displays the total count of threats detected within your selected time period. Selecting any bordered chart within the threat summary sections automatically filters the detailed events table below to display only threats matching the selected category. Clicking the same chart again clears the filter and returns the table to its full view.
The exposure category chart includes visual indicators and support click-through functionality that enables rapid threat categorization and investigation workflow management.
5. Detailed events table
The detailed events table presents comprehensive information for each detected threat, including exposure categories, current investigation status, technical details, and source information. The table supports advanced sorting, filtering, and search capabilities to enable efficient threat triage and investigation workflows.
The table includes specialized category badge components that provide visual indicators for threat types including Credentials, Personal Identifiable Information (PII), and Identity exposures. Each row represents a unique threat event with complete contextual information for security analysis.
The table automatically sorts events by status column with the following priority order: New, In Progress, Remediated, Accepted Risk, and Ignore. This default sorting ensures that newly discovered threats requiring immediate attention appear at the top of the investigation queue.
You can take the following actions from the events table:
- Search across all event data using the search functionality
- Filter events by specific criteria including threat type, status, and source
- Configure which columns display in the table view using the column configuration options
- Export selected events or complete datasets using the comprehensive data export functionality
Status workflow management
The Dark Web Monitoring dashboard implements a comprehensive status workflow system that enables tracking threat events from initial discovery through complete remediation. Each event can be assigned one of five status levels that reflect the current state of investigation and response:
-
New: Recently discovered threats that require initial security assessment and prioritization. These events appear at the top of the sorted table view to ensure immediate attention.
-
In Progress: Threats currently under active investigation or remediation by security teams. This status indicates ongoing work and prevents duplicate effort across team members.
-
Remediated: Completed incidents where the identified threat has been successfully addressed and no longer poses risk to the organization.
-
Accepted Risk: Threats that have been evaluated and determined to be acceptable risks based on organizational risk tolerance and compensating controls.
-
Ignore: Events determined to be false positives, duplicate entries, or otherwise non-actionable threats that should be excluded from active monitoring.
Change State
Follow these steps to change the state of events.
- Select one or more events from the list.
- From the Bulk Actions bar, click Actions > Change State.
- In the Change State dialog box, select a state from the list to assign to the events.
- Click Change State.
6. Event investigation panel
The event investigation panel provides detailed information for selected events through a convenient side panel that opens when you select any row in the detailed events table.
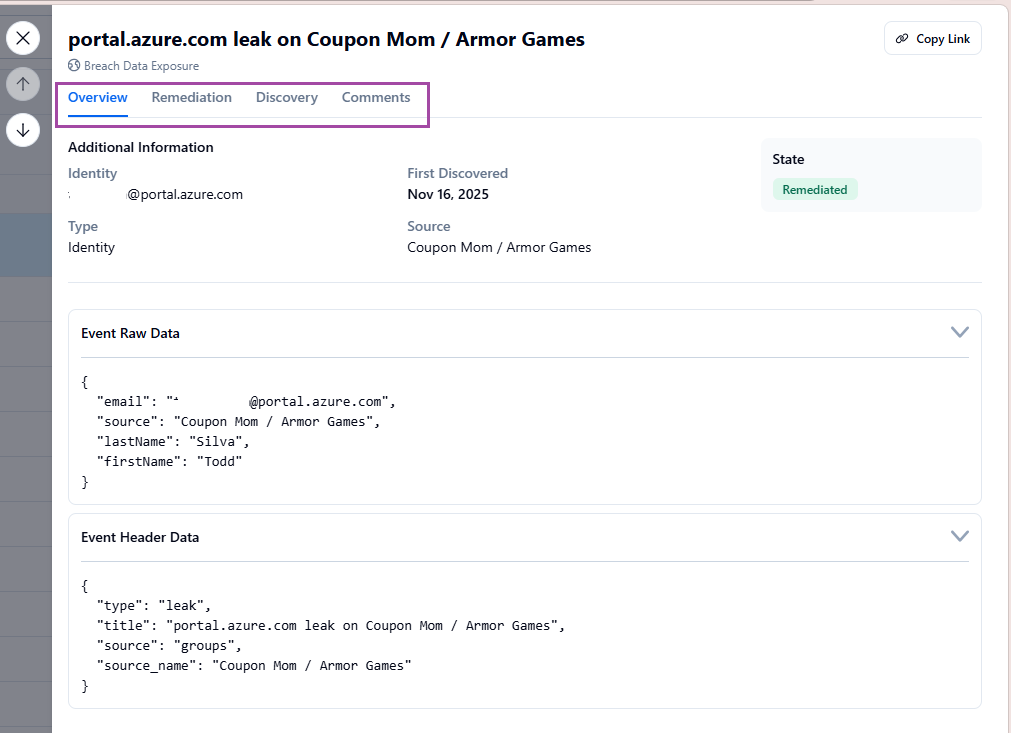
This panel displays comprehensive event details organized across three specialized tabs to support thorough investigation and collaborative response workflows for comprehensive threat analysis.
-
Overview tab: Displays essential event details including the exposure category (such as Public Data Exposure), current investigation state (New, In Progress, Remediated, Accepted Risk, or Ignore), threat type (Source Code, Forum Posts, etc.), source platform (GitHub, Exploit.IN, etc.), metadata including first seen date, and any custom tags applied by users for organizational tracking.
-
Remediation tab: Provides steps to resolve issues when your organization, employees, or subsidiaries are affected by exposed data from breaches, the dark web, or public sources.
-
Discovery tab: Shows the timeline of when the event was discovered.
-
Comments tab: Enables collaborative investigation documentation where team members can add comments, observations, and investigation findings to specific events. This tab also displays comments from other team members, supporting coordinated response efforts and knowledge sharing across security teams.
Getting started with Dark Web monitoring
-
Access the dashboard: Navigate to the Dark Web Monitoring dashboard under External Threats.
-
Review time settings: Examine the current time range setting and adjust if needed to focus on your preferred analysis period. The default "All Time" view provides the most comprehensive threat landscape overview.
-
Analyze threat summary: Review the threat summary charts to understand current exposure levels across dark web sources, breach databases, and public data platforms.
-
Investigate priority threats: Focus on events with New status in the detailed events table, as these represent recently discovered threats requiring immediate security assessment.
-
Use investigation tools: Select specific events to access detailed technical analysis, add investigation notes, and coordinate response efforts using the investigation panel.
-
Track remediation progress: Update event status State as investigations progress and remediation actions a are completed to maintain accurate threat tracking.
Best practices for Dark Web monitoring
Regular review of the Dark Web Monitoring dashboard enables proactive threat detection and response.
- Check the dashboard frequently to identify new threats before they escalate into security incidents.
- Prioritize events by status, focusing first on newly discovered threats that require immediate attention.
Document investigation findings and remediation actions using the collaborative comments feature to maintain institutional knowledge and enable effective team coordination. Update threat status consistently as investigations progress to ensure accurate tracking of organizational security posture.
Use the time-based filtering capabilities to analyze threat patterns and identify trends that may indicate increased risk or successful security improvements. Export threat data regularly for integration with other security tools and for compliance reporting requirements.
The technical event analysis tools provide deep insight into threat attribution and technical indicators, enabling more effective threat hunting and security control validation across your organization's digital infrastructure.